

Searchable News & Info From Reliable Online Sources.
Latest Real News From 140 News Sites Updated Every 15 Minutes.
- Special Report: Cybersecurity Beyond the EAS Box
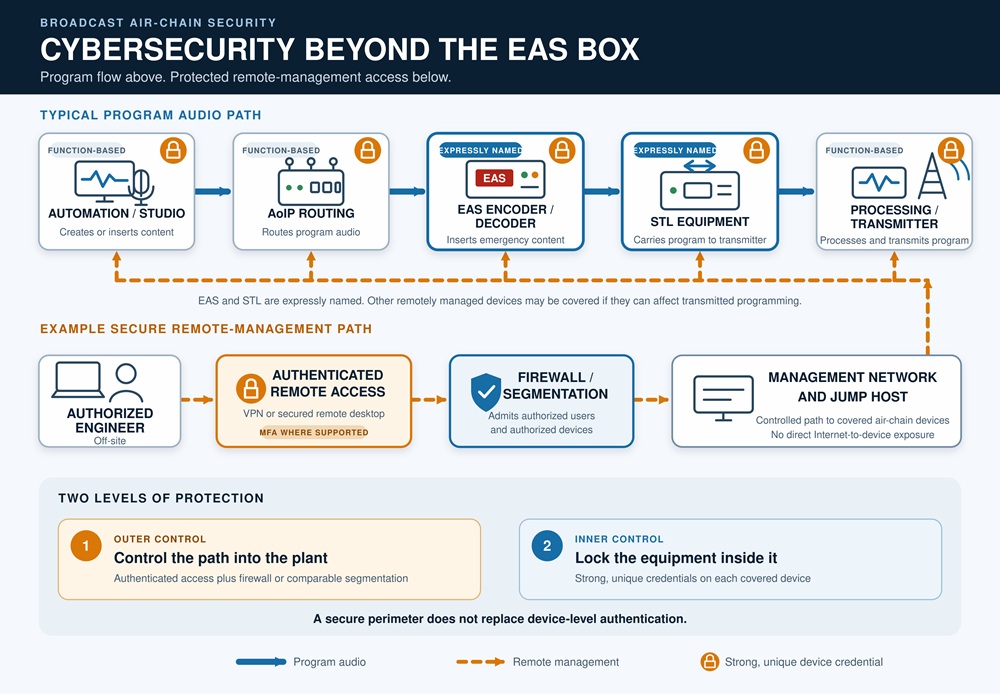
 Click to enlarge. Block diagram setting out the concepts described in the article. The recent FCC order on “EAS cybersecurity” reaches much further into the air chain than its alerting origins suggest. Some of its shortest phrases may require the most work. This article presents 10 things for you to do before the Sept 29 deadline, plus some questions the industry still needs answered. The phrase “EAS cybersecurity” makes this sound like a rule about one box. It isn’t. Yes, it covers the EAS encoder/decoder. It expressly covers STL equipment, too. Then comes the language that should make each of us chief engineers stop and take inventory: remotely managed equipment that routes, processes or inserts content into the programming transmission. In a modern radio plant, that may include automation, codecs, audio processors, remote controls, RDS encoders and a fair piece of the AoIP system. One sentence in Washington can turn into dozens of passwords, several maintenance windows and a long talk with whoever owns the firewall. There is a sound reason for the order. Attackers have reached improperly secured broadcast equipment and transmitted unauthorized audio, including EAS tones and SAME codes. Default passwords, exposed web interfaces and old firmware aren’t harmless shortcuts anymore. The rule takes effect Sept. 29, 2026. It requires strong authentication, prompt installation of security updates and a firewall or comparable segmentation practice that restricts remote management to authorized devices and users. Simple enough on paper. Now take it into the broadcast facility. 1. Separate the final rules from the proposals FCC 26-38 runs 101 pages because it is both a Report and Order and a Further Notice of Proposed Rulemaking. Much of it discusses ideas that aren’t requirements yet, including broader EAS modernization and message authentication. [You can learn more about those separate proposals in Radio World’s four-part series.] The binding cybersecurity language is much shorter. New paragraph 47 CFR 11.35(d) contains the three basic controls: authentication, security updating and restricted management access. The commission did not adopt the proposed requirement for a full cybersecurity risk-management plan. It also declined to require annual certification or reports of unauthorized access. Multifactor authentication, role-based access, backups, incident-response plans and equipment replacement weren’t imposed as universal requirements. Many of those measures are still good practice. But station managers need to know which items are tied directly to the rule and which belong to the station’s larger IT security program.… [TheTopNews] Read More.17 mins ago
- Britain’s golden girl Amy Hunt doubles down in Sydney Sweeney row on GMB
 Amy Hunt has doubled down on her criticism of Sydney Sweeney after she posed naked in a betting advert. [TheTopNews] Read More.19 mins ago
- Emmy winners make history! Four major records broken in one night by Jean Smart,...The 78th Emmy Awards on Monday night featured four record breaking moments, including major wins for Jean Smart, 75, and Alison Janney, 66. [TheTopNews] Read More.20 mins ago
- U.S. Has Deployed Weapons in Space, Air Force Secretary Says
 Troy E. Meink’s comments were the first public acknowledgment of American weapons in orbit. The Pentagon has been preparing for potential conflict in space with Russia or China. [TheTopNews] Read More.21 mins ago
- British Hedge Fund Founder Odey Loses Appeal Against Industry Ban
 Former hedge fund manager Crispin Odey lost his appeal on Monday against an industry ban for hampering an internal disciplinary investigation into sexual harassment allegations, although a fine imposed on him by Britain’s financial watchdog was reduced. A spokesperson for … [TheTopNews] Read More.23 mins ago
1
2
3
…
102
Next »
Click to enlarge. Block diagram setting out the concepts described in the article. The recent FCC order on “EAS cybersecurity” reaches much further into the air chain than its alerting origins suggest. Some of its shortest phrases may require the most work. This article presents 10 things for you to do before the Sept 29 deadline, plus some questions the industry still needs answered. The phrase “EAS cybersecurity” makes this sound like a rule about one box. It isn’t. Yes, it covers the EAS encoder/decoder. It expressly covers STL equipment, too. Then comes the language that should make each of us chief engineers stop and take inventory: remotely managed equipment that routes, processes or inserts content into the programming transmission. In a modern radio plant, that may include automation, codecs, audio processors, remote controls, RDS encoders and a fair piece of the AoIP system. One sentence in Washington can turn into dozens of passwords, several maintenance windows and a long talk with whoever owns the firewall. There is a sound reason for the order. Attackers have reached improperly secured broadcast equipment and transmitted unauthorized audio, including EAS tones and SAME codes. Default passwords, exposed web interfaces and old firmware aren’t harmless shortcuts anymore. The rule takes effect Sept. 29, 2026. It requires strong authentication, prompt installation of security updates and a firewall or comparable segmentation practice that restricts remote management to authorized devices and users. Simple enough on paper. Now take it into the broadcast facility. 1. Separate the final rules from the proposals FCC 26-38 runs 101 pages because it is both a Report and Order and a Further Notice of Proposed Rulemaking. Much of it discusses ideas that aren’t requirements yet, including broader EAS modernization and message authentication. [You can learn more about those separate proposals in Radio World’s four-part series.] The binding cybersecurity language is much shorter. New paragraph 47 CFR 11.35(d) contains the three basic controls: authentication, security updating and restricted management access. The commission did not adopt the proposed requirement for a full cybersecurity risk-management plan. It also declined to require annual certification or reports of unauthorized access. Multifactor authentication, role-based access, backups, incident-response plans and equipment replacement weren’t imposed as universal requirements. Many of those measures are still good practice. But station managers need to know which items are tied directly to the rule and which belong to the station’s larger IT security program.… [TheTopNews] Read More.
17 mins ago
Amy Hunt has doubled down on her criticism of Sydney Sweeney after she posed naked in a betting advert. [TheTopNews] Read More.
19 mins ago
The 78th Emmy Awards on Monday night featured four record breaking moments, including major wins for Jean Smart, 75, and Alison Janney, 66. [TheTopNews] Read More.
20 mins ago
Troy E. Meink’s comments were the first public acknowledgment of American weapons in orbit. The Pentagon has been preparing for potential conflict in space with Russia or China. [TheTopNews] Read More.
21 mins ago
Former hedge fund manager Crispin Odey lost his appeal on Monday against an industry ban for hampering an internal disciplinary investigation into sexual harassment allegations, although a fine imposed on him by Britain’s financial watchdog was reduced. A spokesperson for … [TheTopNews] Read More.
23 mins ago
The Searchable USWebDaily.com and TheTopNews NewsBank Helps You Be Better Informed, Faster! Spread The Word.